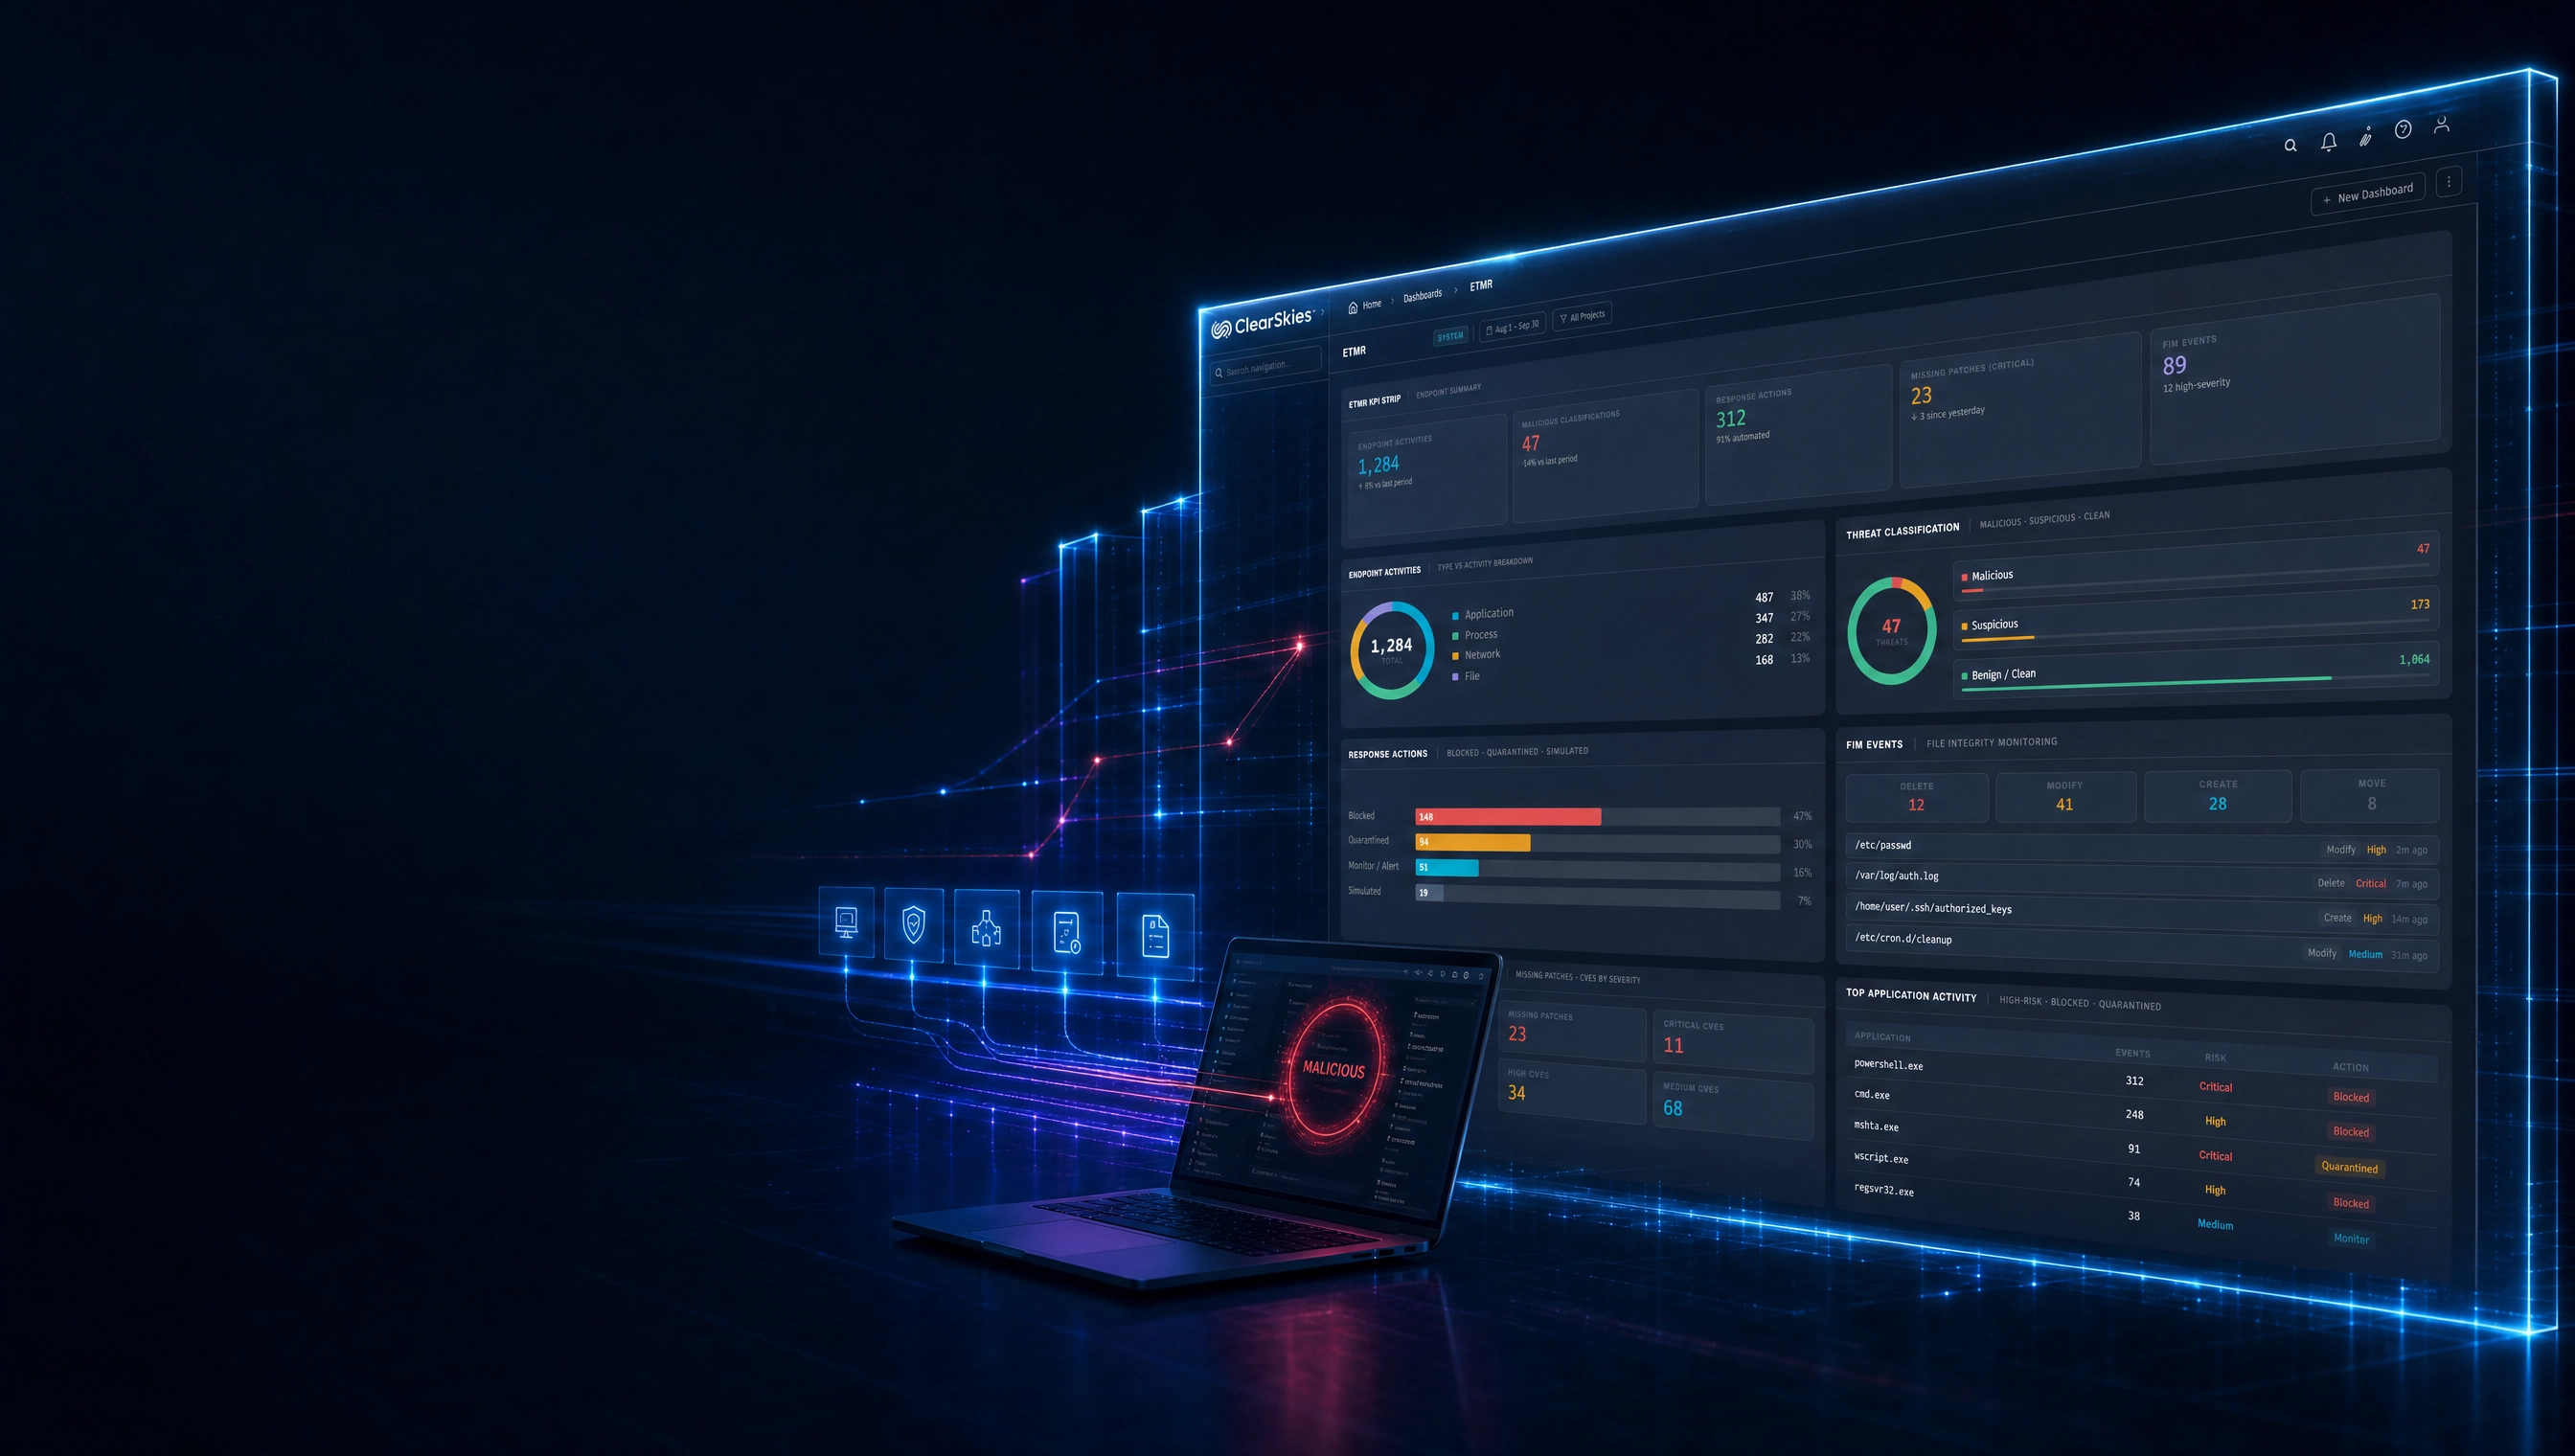
ClearSkies Endpoint Threat Monitoring and Response
Inside the Platform
The add-ons do not exchange intelligence directly with one another.
One engine
Every add-on connects to the engine, none to another
Bidirectional
Verdicts go in, detection outcomes come back
Built for providers
Row-level isolation, per-tier gating, per-tenant quotas
What ETMR contributes
ETMR is one of the six native add-ons of ClearSkies iISOC, deployed with the platform and reporting to the TDIR engine, the orchestration core through which every add-on connects.
Each connects to the engine, which ingests through iCollector, normalizes, correlates and redistributes the result across the platform.
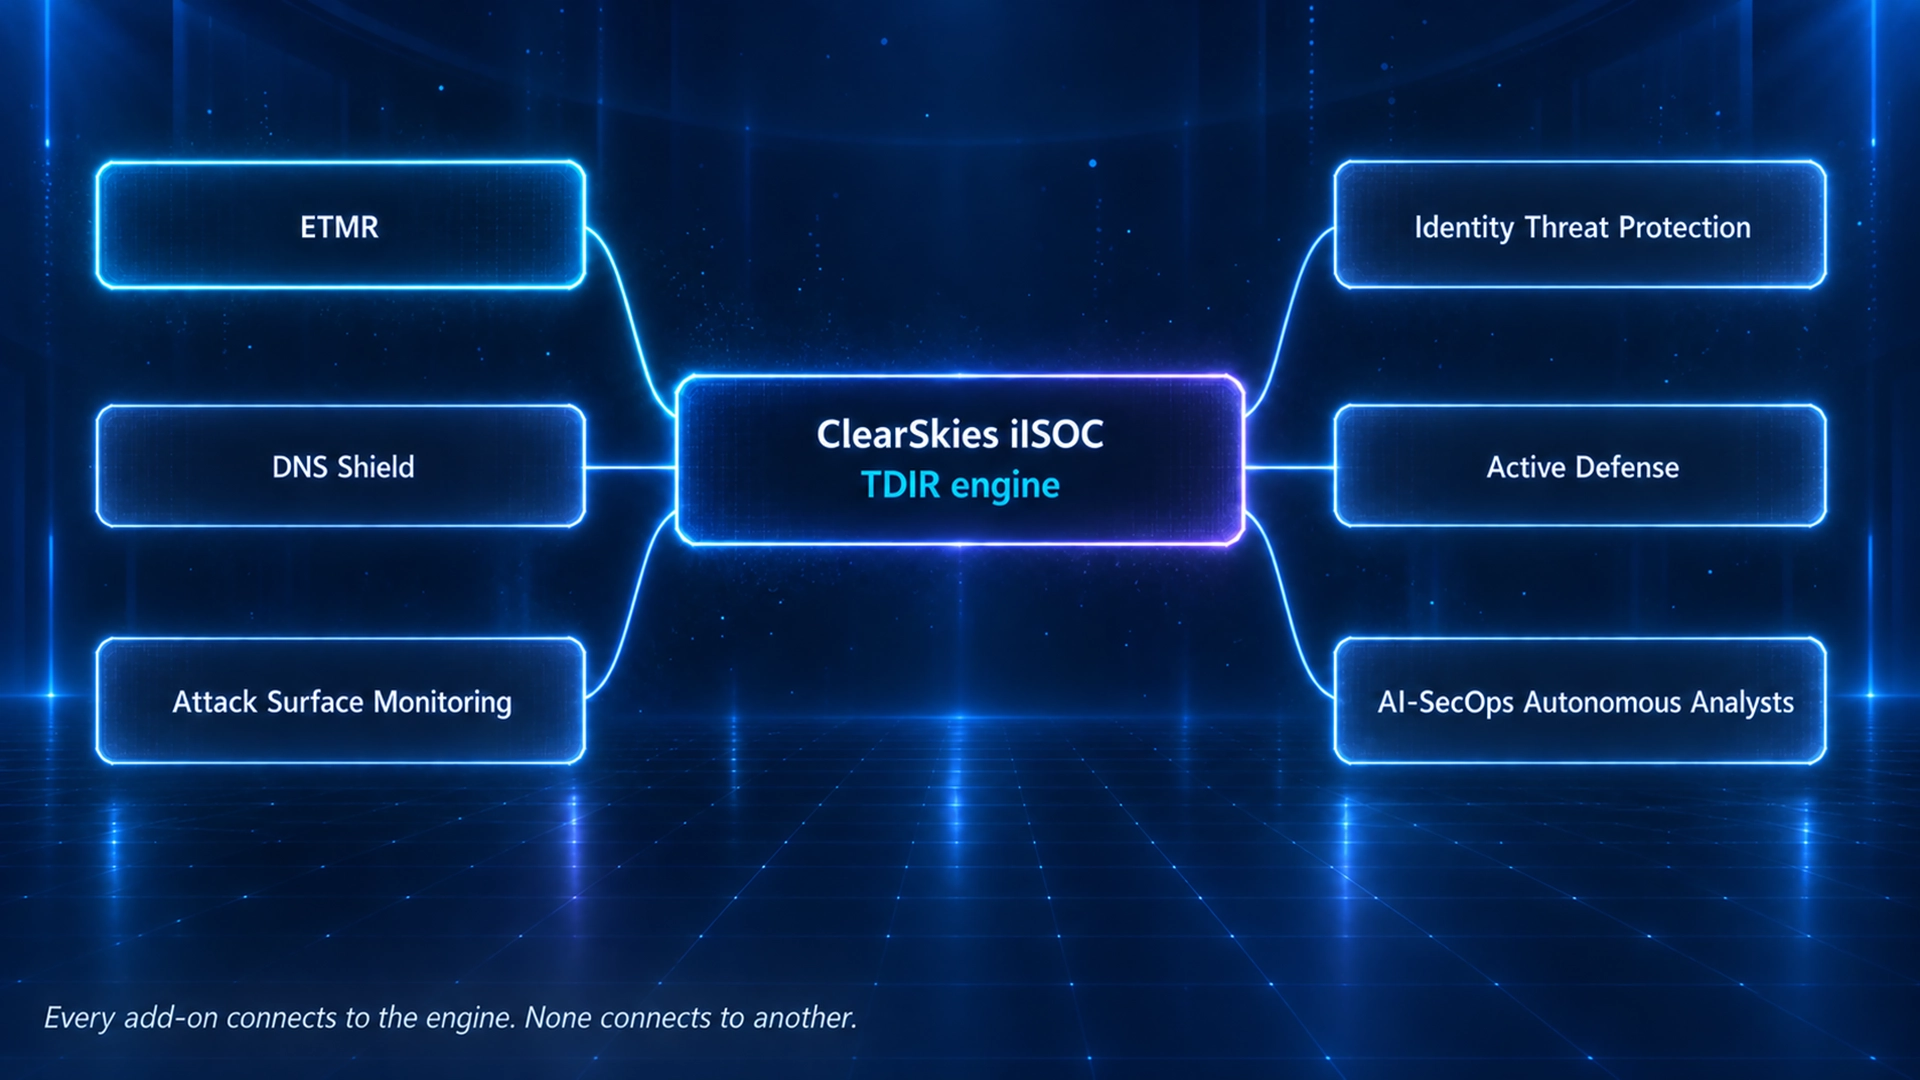
Every add-on connects to the engine. None connects to another.
The signal no other layer can see
The endpoint is where an intrusion becomes concrete. No other layer can see a process spawning a child process, a script writing an executable to a temporary path, or a credential store being read from memory.
| Context | What the analyst receives |
|---|---|
| Without endpoint context | An outbound connection from a host is a moderate signal. |
| With endpoint context | The same alert, annotated with a PowerShell process spawned by a macro-enabled document that wrote an executable to a temporary path and then beaconed at a fixed interval, is a high-fidelity incident an analyst can prioritize immediately. |
That is the signal ETMR contributes: continuous endpoint telemetry, the behavioral verdicts derived from it, and the evidence behind each verdict.
Working with the other add-ons
ETMR never acts on another add-on’s intelligence. When it reports an endpoint-behavior verdict, the engine sharpens that verdict against the other signals it holds.
The engine combines those signals into one picture and drives Active Defense to execute a coordinated response.
The integration is bidirectional
The exchange runs both ways, which is what makes the endpoint part of one system rather than a separate product that happens to send alerts.
ETMR to the engine. Process lineage, file and registry events, user activity and network connections, both as enrichment on existing detections and as detections in their own right, such as a credential-theft attempt or a living-off-the-land execution.
The engine to ETMR. Detection outcomes flow back to the agent. A host under investigation can be isolated automatically, a confirmed-malicious hash or behavior is distributed to every agent as detection content rather than customer data, and an analyst false-positive mark suppresses the noise that produced it.
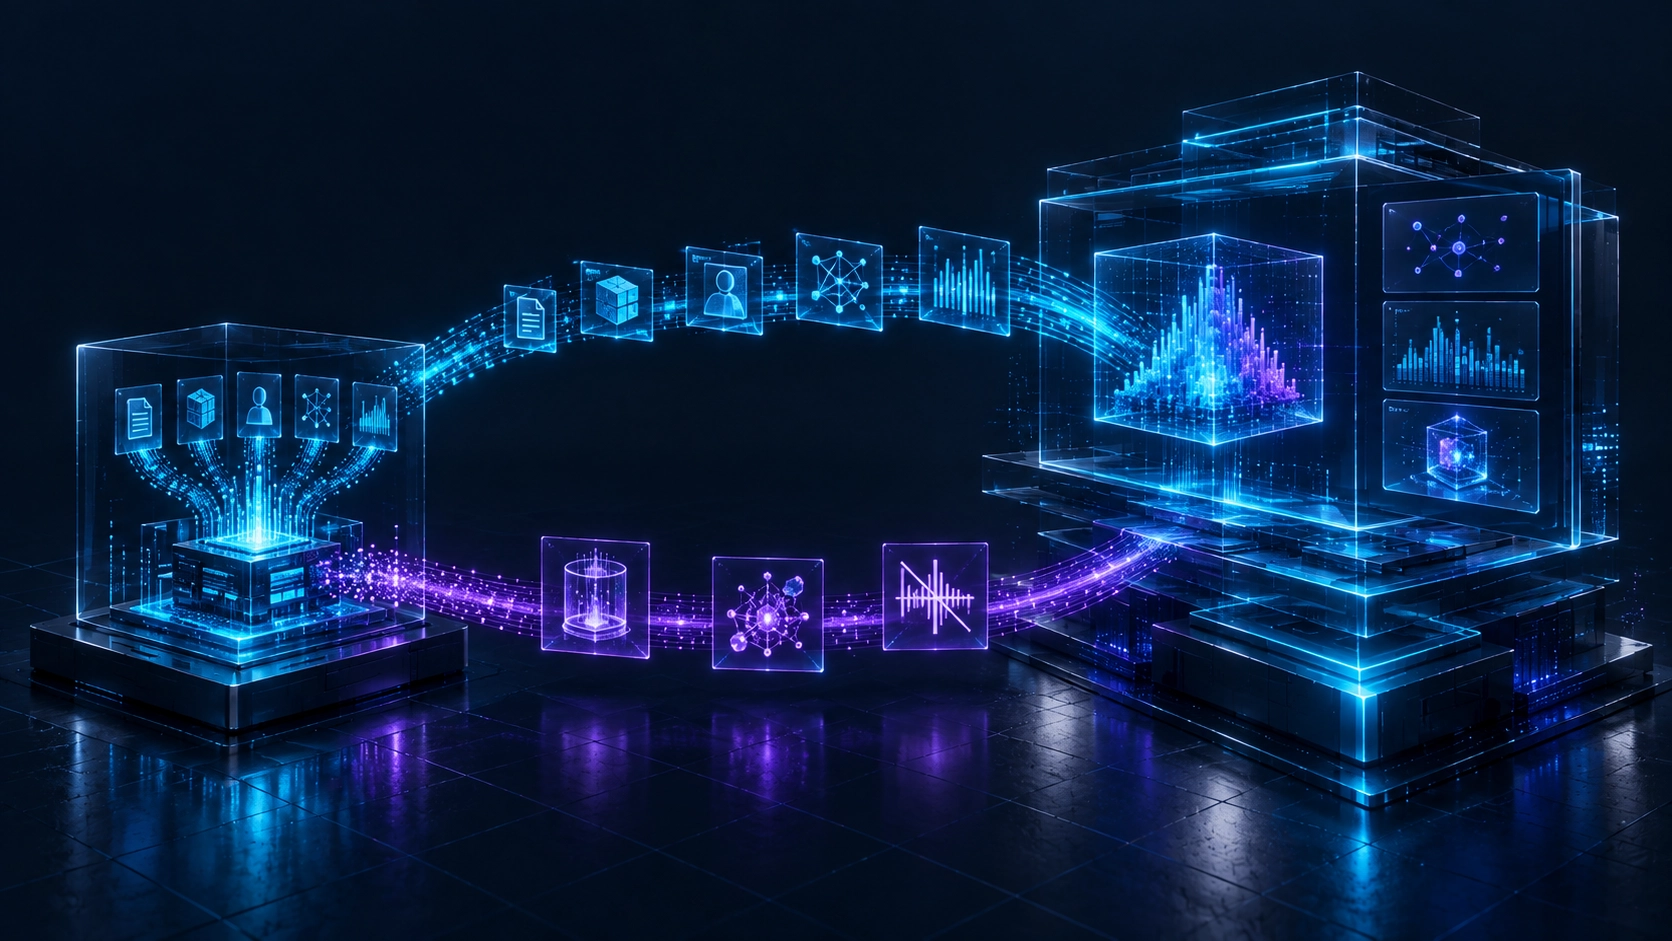
A single endpoint event is enriched by every other layer and, in turn, sharpens them.
Governance and evidence
Endpoint evidence is reported against the frameworks the Regulatory Frameworks core function catalogues, including NIST CSF, ISO 27001, NIS2 and DORA.
Delivering ETMR as a managed service
Multi-tenancy is a first-class concern at every layer, with row-level isolation, per-tier feature gating and per-tenant quotas, so a provider delivers ETMR across many customers from a single deployment. The tenant-pool model scales economics with the customer base rather than licensing one customer at a time.
- One cross-tenant console for endpoint status, alerts and containment actions.
- White-label reporting, so the service carries each customer’s identity.
- Audit-ready reporting built in, for compliance and for the board.
- Behavioral detection absorbs the high-volume work, so analyst time goes to judgment.
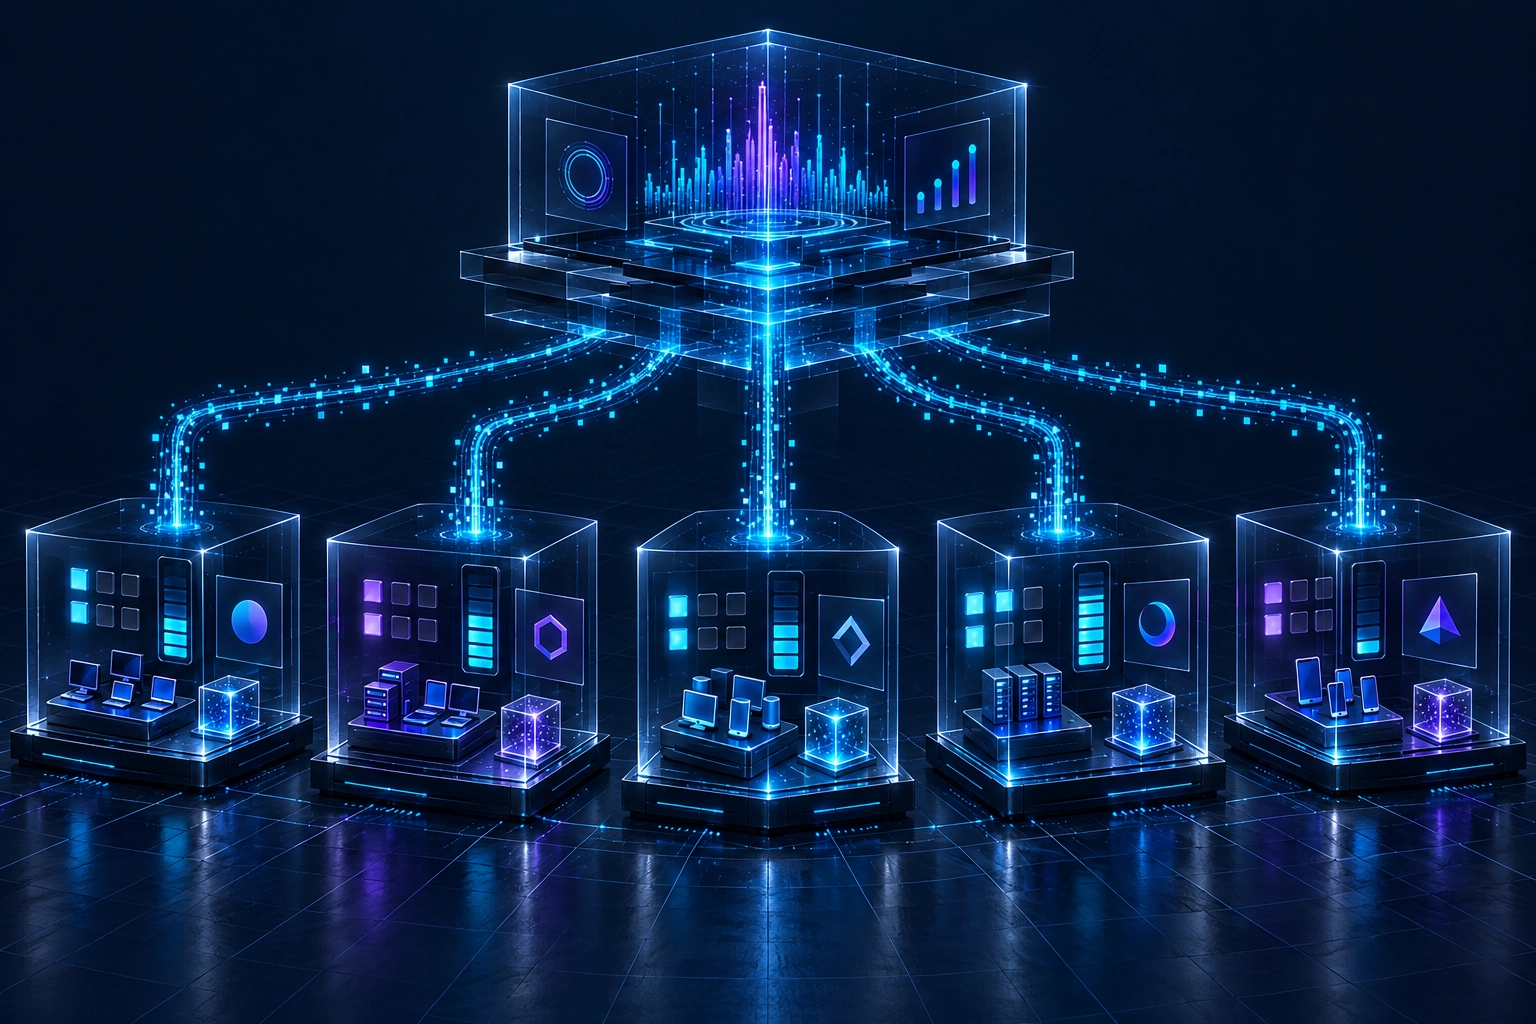
See the whole endpoint, not just the malware.
Because ETMR reports to the engine rather than acting laterally, the same endpoint verdict is reused across every correlation instead of being derived again in each tool.
Request a Demo