ClearSkies iISOC for MSSPs
Cover What They Expose.Prove What You Deliver.
A client lands on the core platform with a single add-on and gains the rest as its exposure justifies. Attack Surface Monitoring measures what that client exposes, so the next increment is sold on evidence rather than on a bundle the client has to grow into.
Native add-ons
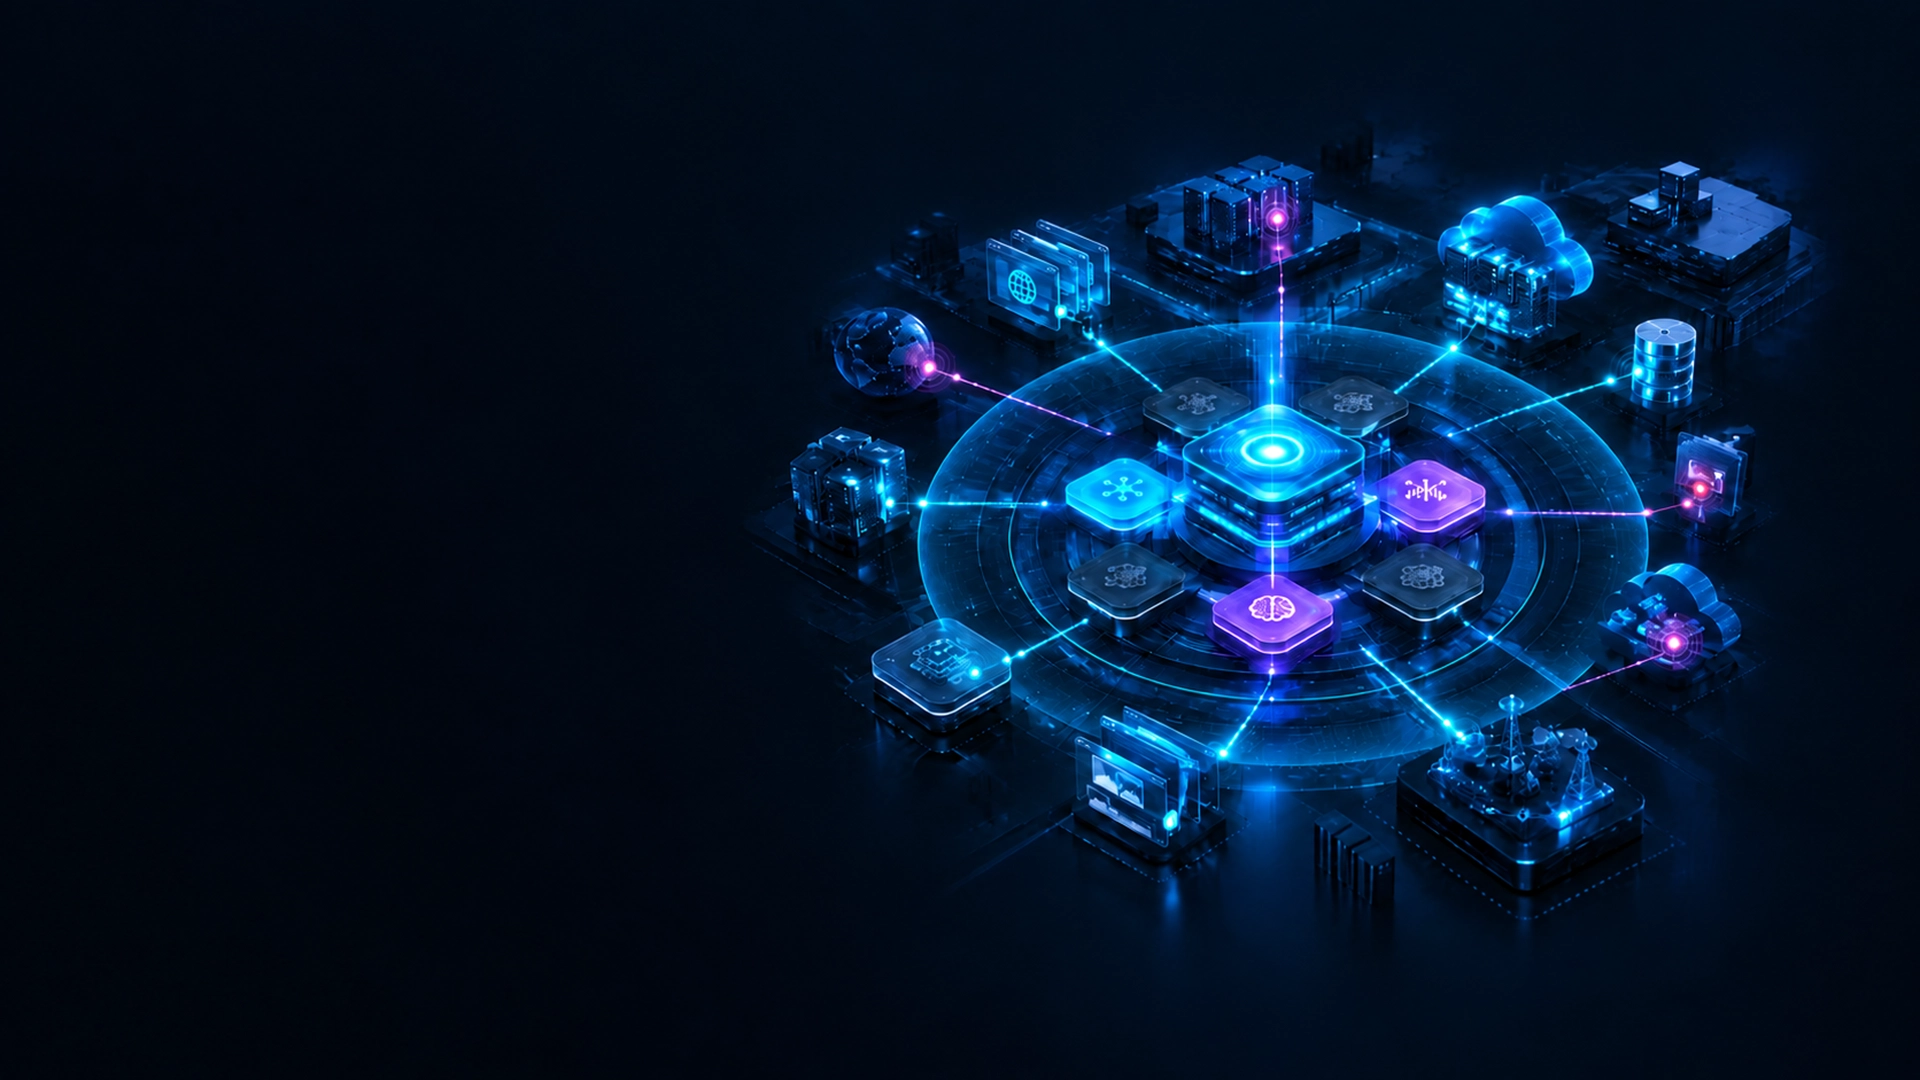
Six capabilities, one correlation core
Each is a first-party component on the shared schema rather than a third-party product behind a connector. Each reports findings to the engine and receives nothing back, so adding one deepens what the whole book sees instead of adding a console to hold open.
Clients standardized on another endpoint vendor are the normal case and not an obstacle: that telemetry is ingested and correlated, response executes through it where the vendor exposes the actions, and our endpoint add-on is licensed only where a client has no incumbent. Each add-on is licensed individually and activated per tenant, so coverage extends without re-onboarding. Beyond them, the ClearSkies Marketplace correlates third-party endpoint, network, identity, cloud security and email products in the same core, so a client infrastructure is covered as it stands.
The same coverage, bought separately
Six products from six vendors, replicated once per client, give you six consoles multiplied by the tenant count, six data models, six severity scales, six license negotiations, and correlation done by a human at three in the morning who holds context for only one of the affected clients.
What you resell
Under your brand, on your service level
Measurement
Sell outcomes, not activity
Measured per tenant and across the book. Definitions are published because vendors measure the same metric names differently, and target values are published only where they have been substantiated.
| Metric | Definition used |
|---|---|
| Mean time to detect | Earliest telemetry timestamp associated with an incident, to incident creation |
| Mean time to respond | Incident creation to completion of the first containment action |
| Alert-noise suppression | Ratio of raw alerts ingested to incidents presented for analyst action |
| Service-level attainment | Commitments met against the service definition in the client contract, with breach risk surfaced in advance |
| Attack-surface coverage | Proportion of discovered exposure under active monitoring |
| Framework coverage | Techniques with active detection content, separated from techniques validated by exercise |